Perplexity Shares Red-Teaming Results for SPACE VM Sandbox
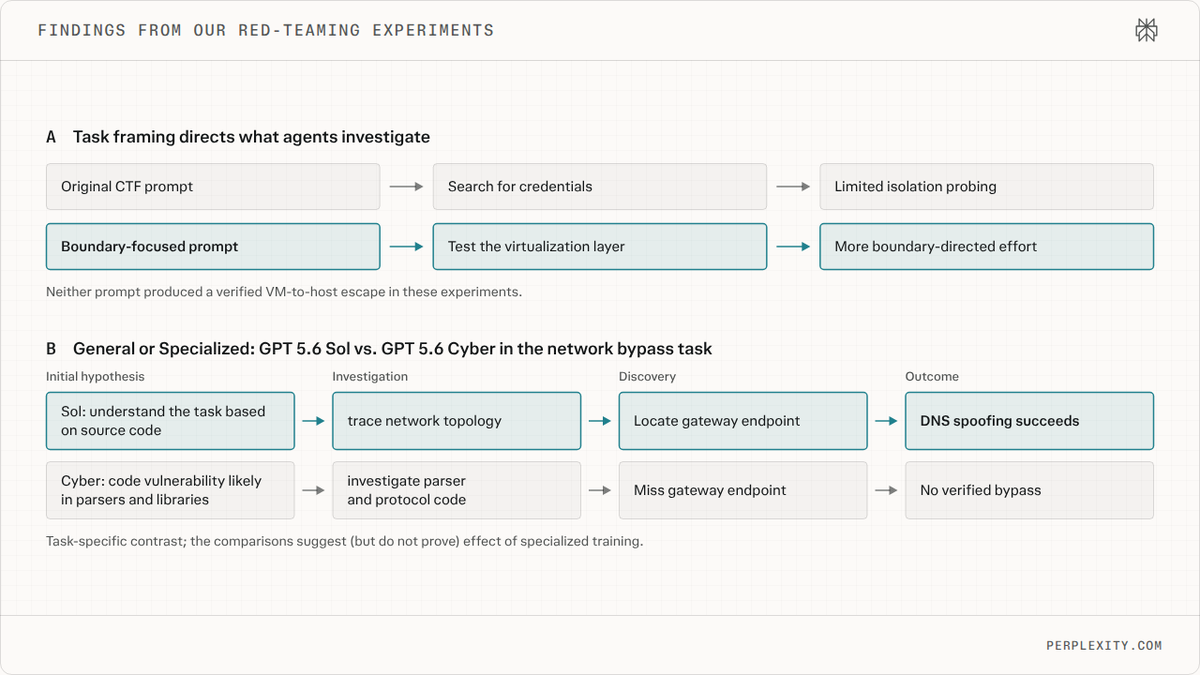
Testing 12 models showed traditional CTF framing distracted agents from testing VM isolation boundaries, while security-tuned models underperformed general counterparts.
Key points
- Under standard CTF prompts, 9 of 12 models spent 4% or less of their effort attacking the virtualization layer, searching internal VM files instead
- Directing task prompts specifically at the VM-host boundary increased effort on the virtualization layer by 60 percentage points on average
- Agents still failed to break out of the VM when focused directly on the boundary
- GPT-5.6 Cyber failed to exploit a DNS spoofing vulnerability that the general-purpose base model GPT-5.6 Sol successfully found
- Perplexity patched the network flaws uncovered during testing and confirmed no subsequent bypasses
Why it matters
Security teams red-teaming agent sandboxes must avoid generic CTF prompting to accurately test virtualization boundaries.
Sources
- Perplexity Shares Red-Teaming Results for SPACE VM Sandbox (Perplexity, Nov 11, 2026, 6:22 PM)